Daniel Alfocea's Picture

Daniel Alfocea, known for years as cr0hn

Twenty years turning technical complexity into clear decisions. I used to build and break systems; now I help decide what to do with them.

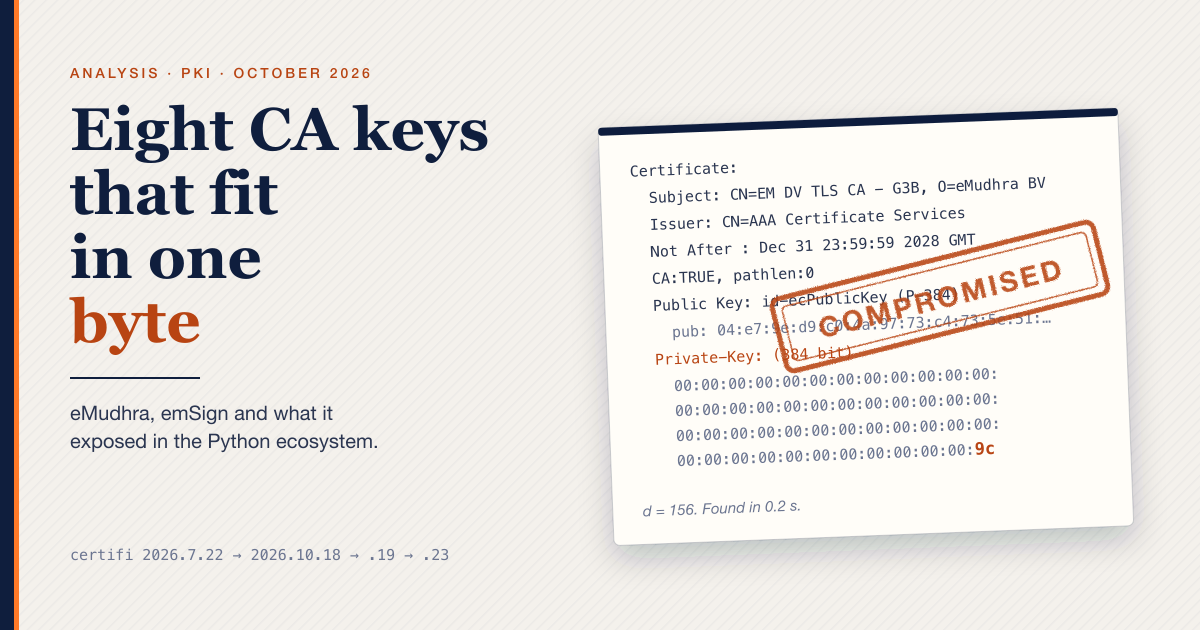
Eight CA keys that fit in one byte: the eMudhra incident and what it exposed in the Python ecosystem

Analysis of the compromise of eMudhra's emSign intermediates: how the keys are recovered from the certificate itself, why certifi had to remove whole roots, which versions of certifi, pip, uv and CPython protect you, and why Apple's curl, git and python3 still trust them.
The October 29 Binance theft: 50 signatures, one lucky nonce and a hot wallet that stopped being theirs

On-chain analysis of the Binance 14 hot wallet drain with EIP-7702: the type 4 transaction with 50 authorizations, the disassembled sweeper, the flow of funds and what exchanges and custodians need to change.

Slow JSON Stream: 64 connections at 1 B/s takes down PHP/Laravel in under 2 minutes

New DoS attack: 37/41 HTTP frameworks vulnerable by default. 64 connections at 1 byte/s exhausts PHP/Laravel in <2 min. Full PoC + paper + Docker testbed included.

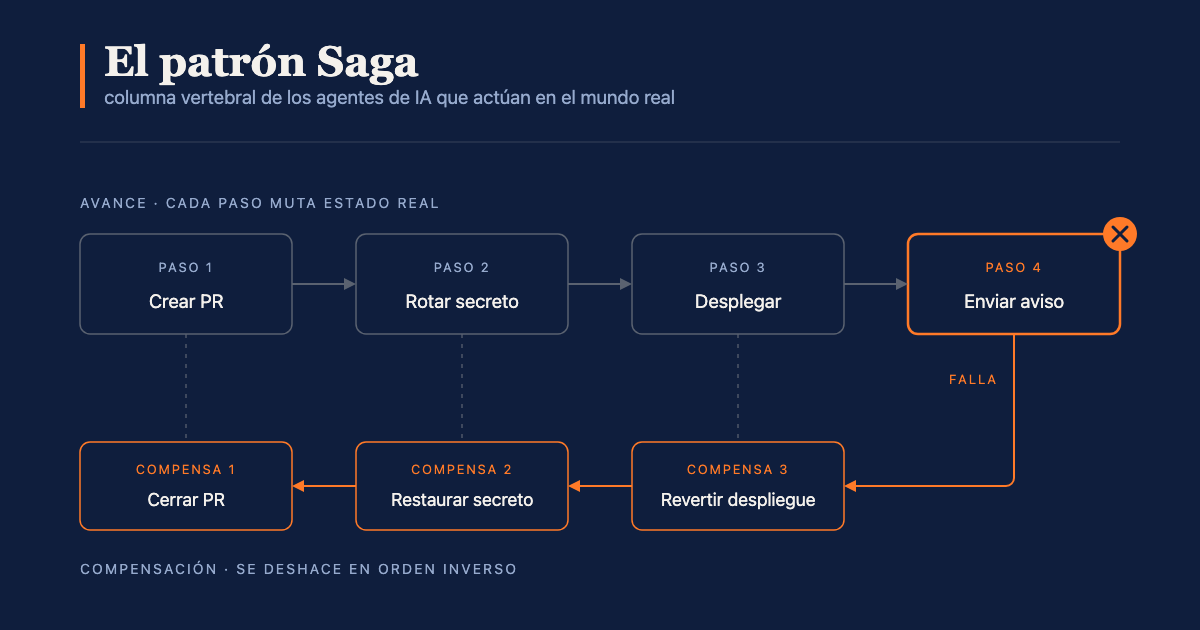
The Saga pattern as the backbone of AI agents that act in the real world

An AI agent doesn't reason, it acts. And when it acts on real systems, you need Saga. Not as an architectural fashion, but as a philosophy of responsibility.

Supabase Auth vs Auth0: The Lie of Easy Authentication and the Real Risk

If you think wiring up OAuth2 with Google is easy, read this before you walk into a mess you won't know how to walk out of. A brutal comparison between Supabase Auth and Auth0.